

@pmarketresearch
- Followers 0
- Following 0
- Updates 5116
PW Consulting: Anti‑Tamper Software Market Poised to Grow at 15% CAGR Through 2032

Anti‑Tamper Software Market — 2026 Strategic Briefing for Enterprise Leaders
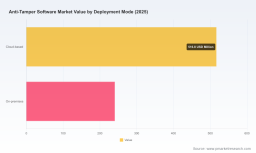
PW Consulting’s new Anti‑Tamper Software Market report synthesizes six years of historical analysis (2020–2025) and an actionable 2026–2032 forecast to equip security, product, and procurement leaders with the intelligence required to make confident investments in application and device integrity. The macro trajectory is clear: the market is expanding rapidly, with a 15.0% compound annual growth rate embedded in our base case. Measured in USD (Million), global market value climbs from the 2025 base to roughly two billion USD by 2032 under the forecast scenario — a scale that changes how organizations should prioritize anti‑tamper in their 2026 roadmaps.
Anti Tamper Software Market
Why 2026 is a Pivotal Year
Two converging forces make 2026 decisive for anti‑tamper adoption. First, the threat environment continues to evolve: adversaries targeting mobile, cloud‑native, IoT, automotive, and gaming assets are applying automation, supply‑chain techniques, and commoditized exploitation tools that amplify the impact of single‑point weaknesses. Second, regulatory and program protection pressures are rising. DoD directives and program protection instructions, growing state privacy regimes in the U.S., and sectoral compliance regimes (finance, healthcare, government) mean that anti‑tamper measures are increasingly part of procurement, export control, and compliance checklists—not optional afterthoughts.
Anti Tamper Software Market
For enterprises that must balance speed‑to‑market with preservation of IP and operational integrity, 2026 should be treated as a planning inflection: selectivity in tooling, rigorous integration discipline, and measurable ROI will separate successful programs from underperforming pilots.
Anti Tamper Software Market
Report Highlights — Practical, Operational, Ready for Execution
This report is not a catalog of vendor logos; it is a playbook. We designed the content for teams that will implement, operate, and procure anti‑tamper protections over the next 18–36 months. Key deliverables include:
- Actionable implementation playbooks that map anti‑tamper techniques (obfuscation, runtime application self‑protection, white‑box cryptography, environmental checks, hardware sensors) to development pipelines and CI/CD gates.
- Procurement and RFP templates tailored to different buyer personas—SaaS platforms, mobile product owners, SoC teams, and critical infrastructure operators—each aligned to measurable acceptance criteria.
- Integration checklists and DevSecOps staffing models that quantify the specialist skills required for RASP, AI‑enabled tamper detection, and continuous monitoring to reduce deployment friction and lifecycle cost overruns.
- Risk and ROI frameworks that translate protection choices into expected incident reduction, reduced remediation cost, and program protection outcomes—framed so CISOs, CFOs, and product owners can make investment tradeoffs.
- Operational playbooks for high‑risk verticals, including gaming, media, finance, automotive/IoT, and regulated healthcare/government contexts—each with tailored validation plans for field testing and telemetry verification.
- Vendor selection scorecards and a defensible short‑listing process that emphasize integration risk, update cadence, compatibility with native toolchains, and supply‑chain considerations.
Strategic Implications for Enterprise Decision‑Makers
- Elevate anti‑tamper from an engineering checkbox to a cross‑functional program. Our analysis shows rising demand for end‑to‑end integrity assurance: procurement, legal, product, and security must coordinate on SLAs, export control posture, and incident response playbooks.
- Design for maintainability. Anti‑tamper controls that cannot be updated without disrupting customer experience or requiring complex rebuilds will fail. Emphasize solutions that support staged rollouts and telemetry‑based validation.
- Plan for specialized talent. Advanced protections require DevSecOps practitioners experienced in runtime instrumentation, cryptographic key management, and threat telemetry. Account for hiring, upskilling, or managed services in 2026 budgets.
- Be pragmatic on coverage. Not all code needs maximal obfuscation; deploy a risk‑based matrix to allocate stronger protection to IP and code paths where tampering yields outsized harm.
- Treat hardware and software anti‑tamper as complementary. For organizations building SoCs or high‑value embedded devices, combine digital shielding with sensor‑based and active countermeasure designs.
Competitive and Vendor Dynamics — What We Profile
The competitive landscape is dynamic, populated by specialized application shielding vendors, broader DRM and security platform providers, and players focused on hardware anti‑tamper. PW Consulting’s report provides vendor profiles, capability matrices, and integration considerations for market leaders and emerging challengers. Among the organizations we analyze in depth are:
- Digital.ai (Boston, Massachusetts, USA) — advanced in‑app protection across mobile, IoT, web, desktop, and enterprise applications, with code obfuscation, white‑box cryptography, integrity management, and RASP capabilities.
- Guardsquare (Leuven, Belgium) — mobile‑focused hardening, known for multilayered obfuscation and runtime protection for Android and iOS ecosystems.
- Verimatrix (Meyreuil, France) — application shielding and anti‑tamper technologies for media, mobile, and enterprise contexts (recent portfolio movements are reshaping options in 2026).
- Appdome (Boston/Redwood City area, USA) — no‑code mobile security platform emphasizing automated anti‑tamper and fraud prevention, attractive to organizations seeking rapid adoption without heavy engineering lift.
- Irdeto (including Denuvo) — combines software protection with anti‑piracy mechanisms, notable for gaming and media protection approaches and embedded application shielding.
- Specialists and hardware‑oriented vendors — Secure‑IC, Rambus and others offering anti‑tamper IP, cryptographic cores, and hardware countermeasures for high‑assurance environments.
- Breadth providers — companies such as PreEmptive Solutions, Waratek, OneSpan, Pradeo, Promon, Intertrust and PACE Anti‑Piracy—each occupying niches from .NET/Java obfuscation to runtime protection and DRM integration.
Our vendor assessments go beyond feature checkboxes. We evaluate integration friction, SDK lifecycle management, support for automated build systems, telemetry fidelity for tamper detection, and the commercial terms that matter to enterprise buyers (maintenance windows, patching cadence, and upgrade paths).
Recent Market Movements and Signals
- Strategic asset realignments are impacting the vendor field. Notably, late‑2025 and early‑2026 transactions and asset transfers have reshaped portfolios and created new bundling opportunities—this requires buyers to reassess roadmaps and integration plans in 2026.
- Recognition and momentum signals from customer‑review platforms indicate increasing buyer preference for no‑code, low‑touch solutions for specific mobile use cases, supporting rapid pilots that can be transitioned into production with defined SLAs.
- Hardware anti‑tamper innovation (including IP for SoCs and analog tamper detection) is moving from R&D into commercial availability, widening protection choices for device OEMs and Tier‑1 integrators.
Regulatory and Program Protection Context
Policy frameworks are shaping procurement and acceptance criteria. U.S. Department of Defense anti‑tamper directives and program protection instructions emphasize deterrence and control for defense‑critical technologies. In commercial contexts, anti‑tamper capabilities increasingly support compliance with sectoral regulations—helping firms demonstrate reasonable controls for SOX, HIPAA, and federal information security obligations. At the same time, emergent state‑level privacy laws increase the reporting and compliance footprint, raising the bar for how protection controls are audited and validated.
How Buyers Should Use This Report in 2026
- Use the report’s RFP templates and vendor scorecards to run parallel pilots with objective telemetry measurement—don’t buy on feature claims alone.
- Adopt the included TCO and ROI frameworks to justify budget — quantify incident avoidance, maintenance costs, and operational overhead when evaluating solutions.
- Follow the stepwise integration checklists to reduce rollout risk: sandbox validation, staged deployment, telemetry correlation with backend fraud systems, and a documented rollback plan.
- Prioritize vendor support for continuous delivery: ensure SDKs and protection artefacts can be updated without costly rebuilds or customer disruption.
Next Steps & Where to Access Full Intelligence
PW Consulting’s Anti‑Tamper Software Market report contains the granular segmentation, vendor rankings, implementation artifacts, and financial models necessary for board‑level decisions and tactical program launches. The executive briefing above is designed to be a concise guide — for deeper segmentation, regional and vertical analyses, granular vendor scorecards, and downloadable implementation templates, please consult the full report on PW Consulting’s research portal. The full dossier contains the detailed splits and proprietary datasets that enterprise programs will use to finalize 2026 investment decisions.
In an era where software and device integrity materially influences competitive advantage, supply‑chain risk, and regulatory standing, the right anti‑tamper strategy is both defensive and strategic. PW Consulting’s report gives you the frameworks, vendor insight, and operational tools to convert protection into a measurable business outcome.
For detailed analysis of this topic, please visit the official page: Anti Tamper Software Market
Lacy Lee
Senior Marketing Manager
sales@pmarketresearch.com
00852-95632430
PW Consulting: www.pmarketresearch.com