

@pmarketresearch
- Followers 0
- Following 0
- Updates 5116
Commercial Encryption Products Market: Why 13.5% CAGR and 15B Scale Redefine Security Strategy by 2032

The Commercial Encryption Products Market: Strategic Trends and Commercial Opportunities
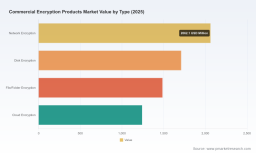
The commercial encryption products market has evolved from a niche cybersecurity concern into a foundational layer of digital infrastructure. By 2025, the market has reached an estimated 6.5 billion USD in revenue, with consistent compound annual growth of 13.5 percent projected through 2032. Over the five-year historical window from 2020 to 2025, revenue expanded by nearly 87 percent, reflecting a structural shift rather than a temporary surge. The trajectory ahead points to continued acceleration, with forecasts suggesting the market will exceed 15.7 billion USD by the end of the forecast period. This growth is not evenly distributed across product types or sectors, but the overall magnitude signals that encryption has moved from compliance-driven procurement to strategic investment.
Several characteristics define the current market landscape. The ecosystem remains moderately concentrated, with the top three players capturing roughly a third of total revenue and the top five accounting for just under 43 percent. This concentration leaves substantial room for specialization, regional differentiation, and niche innovation, particularly in segments where performance, assurance, and integration matter more than price. At the same time, the market faces a pivot point driven by certification transitions, quantum readiness expectations, and the growing mismatch between legacy architectures and cloud-native workloads.
Hardware Encryption Devices Market
Key Challenges and Inflection Points
One of the most consequential challenges is the regulatory transition from FIPS 140-2 to FIPS 140-3. The formal move of FIPS 140-2 certificates to a historical list in September 2026 forces commercial encryption products and the systems that embed them to adopt validated modules under the newer standard. For vendors, this is not a simple recertification exercise; it requires re-architecting validation footprints, aligning engineering roadmaps, and addressing procurement cycles that may stall until compliance is confirmed. For buyers, the risk is procurement inertia: legacy deployments that were once acceptable may face audit exposure or sourcing constraints, while new projects must specify FIPS 140-3 from the outset.
A second inflection point is the post-quantum cryptography transition. NIST finalized post-quantum standards in 2024, and CISA published product categories to support adoption in commercial technologies in early 2026. The market is not yet in full implementation mode, but the direction of travel is clear: organizations are beginning to inventory cryptographic dependencies, assess migration paths, and evaluate vendor roadmaps. The challenge is twofold. First, the technical complexity of hybrid deployments and crypto-agility introduces integration risk. Second, the absence of mature commercial tooling and testing frameworks means early movers must navigate uncertainty around interoperability, performance, and total cost of ownership.
A third challenge lies in workload dispersion. Encryption is no longer confined to perimeter networks or on-premises storage. Data protection requirements now span distributed cloud environments, hybrid identity architectures, edge devices, and payment ecosystems that must balance assurance with latency and throughput. Suppliers that cannot offer scalable key management, integration with cloud services, and modular assurance profiles will find themselves squeezed by both performance requirements and procurement expectations. The markets leading players are responding with certification breadth, cloud-optimized hardware, and software-centric data protection, but the structural tension between assurance depth and deployment agility remains unresolved.
Key Drivers Shaping Market Momentum
Market growth is being propelled by a convergence of technical, regulatory, and demand-side forces. The most visible driver is cryptographic assurance modernization. The shift toward FIPS 140-3 and the emergence of post-quantum standards are reshaping specification language and procurement requirements. Recent vendor activity makes this acceleration tangible. Utimaco achieved FIPS 140-3 Level 3 certification for its u.trust GP HSM Se-Series in May 2026, positioning the company as the only vendor with full FIPS 140-3 coverage across general-purpose and payment HSM portfolios. In December 2025, Thales secured NATO Secret classification for its Luna Network HSM 7 alongside FIPS 140-3 Level 3 validation. These milestones illustrate how high-assurance certification is becoming a competitive differentiator, especially in environments where data sensitivity spans commercial, government, and defense-adjacent use cases.
Demand-side behavior is changing in parallel. Enterprise data protection strategies are shifting from perimeter-based controls to pervasive, identity-aware encryption integrated with broader data security platforms. Regulatory exposure in financial services, healthcare, and public-sector operations continues to raise the baseline for key management and data-at-rest protection. At the same time, business leaders are pressing for faster deployment cycles, cloud-native integration, and reduced operational friction. The result is a market that values not only cryptographic strength but also manageability. Certification becomes a proxy for trust, and trust becomes a procurement gate.
Supply-side dynamics are increasingly shaped by cloud adoption and partnership models. Hardware security modules are no longer treated as standalone appliances in every context. Cloud-optimized HSM families are being selected to support managed cloud HSM services, extending encryption capabilities into elastic environments while maintaining key isolation. Marvell's LiquidSecurity HSM family, chosen by Microsoft for Azure Cloud HSM services in August 2025, reflects this pattern. The broader implication is that encryption infrastructure is being embedded into platform ecosystems, not simply layered as an independent product. For commercial encryption providers, this opens opportunities in integration design, attestation, and managed key services, but it also requires tighter alignment with cloud vendor roadmaps and operational expectations.
Emerging Influences Across the Ecosystem
Three additional dynamics are reinforcing these drivers. First, crypto-agility is moving from a technical aspiration to a procurement criterion. Buyers are increasingly interested in architectures that can adapt to evolving algorithms without wholesale replacement, especially as post-quantum migrations are planned. Second, product certification breadth is expanding beyond traditional enterprise and financial use cases into IoT and connectivity domains. The April 2026 announcement of FIPS 140-3 validation for cryptographic modules on Digi Accelerated Linux-based IoT and connectivity solutions signals that assurance requirements are reaching edge and embedded environments where security has historically been harder to standardize. Third, geopolitical and sector-specific assurance needs are creating differentiated demand. Classification achievements such as NATO Secret for select HSM products illustrate that high-assurance commercial encryption can unlock adjacent markets where data sensitivity and supply-chain trust are paramount.
PW Consulting Information & Electronics Research Center
Together, these drivers are pushing the market toward a more layered structure: certified hardware for high-assurance root operations, software and platform capabilities for data protection and key lifecycle management, and cloud-integrated services for scalability. Growth will be determined not only by how many organizations buy encryption products, but by how many can absorb them into workflows without compromising performance, compliance, or operational continuity.
Competitive Landscape and Leading Strategies
The competitive environment is defined by a handful of established players with strong certification portfolios and a growing emphasis on integration with enterprise and cloud ecosystems. Thales Group maintains a broad commercial encryption and key management position through Luna Network HSMs, payShield payment HSMs, and CipherTrust data security solutions, with recent validation activity reinforcing its high-assurance credentials. Utimaco has concentrated on full-portfolio FIPS 140-3 coverage across general-purpose and payment HSMs, a differentiating posture in markets where procurement teams want a single, consistently validated vendor footprint. Entrust continues to anchor its commercial position in nShield HSMs for key protection, code signing, and enterprise encryption, appealing to organizations that value high-assurance key use cases within broader identity and data protection strategies.
Homomorphic Encryption Market
Futurex occupies a manufacturing-centric positioning with FIPS 140-2 Level 3 and PCI HSM validated products produced in the United States, an advantage in contexts where supply-chain provenance and domestic manufacturing are evaluation factors. IBM brings encryption software, Guardium data protection, and HSM offerings into the enterprise commercial data protection conversation, leveraging platform adjacencies and data security integration. Microsoft competes in a different layer of the stack, with Azure Key Vault and encryption services that incorporate HSM-backed key management for cloud data protection, effectively embedding encryption into a broader cloud platform. Marvell contributes cloud-optimized HSMs, notably through its selection for Azure Cloud HSM services, aligning hardware capability with hyperscale deployment requirements.
Strategic Positioning and Differentiation
Across these players, differentiation is emerging along several axes. Certification scope is one of the most visible. Vendors that can demonstrate consistent FIPS 140-3 validation, payment HSM validation, or elevated classification may secure preference in regulated environments where audit confidence is directly tied to specification language. Product breadth is another axis: players offering both general-purpose and payment HSMs, or hardware combined with software data protection, can address multiple procurement categories within a single relationship. Integration capability is becoming equally important. The ability to connect key management to cloud services, enterprise identity, and data security platforms reduces operational friction and strengthens the value proposition beyond raw cryptographic assurance.
Manufacturing origin and supply-chain narrative also matter in specific segments. Domestic manufacturing, transparent validation histories, and clear product category alignment can influence procurement decisions in government-adjacent, critical infrastructure, and payment environments. At the same time, cloud-native deployments are rewarding providers that can offer modular, scalable hardware or managed services that fit into elastic architectures rather than rigid appliance models.
Structural Evolution in the Market
The market is likely to evolve through both consolidation and niche differentiation. Larger platforms with broad data security, identity, and cloud ecosystems may expand their encryption footprint through product integration or selected partnerships. At the same time, specialized vendors with focused certification portfolios, strong payment or HSM credentials, and clear supply-chain value can thrive by serving high-assurance segments that are less price-elastic. New entrants are unlikely to displace incumbents through pure scale, but they may carve out positions in specific use cases such as cloud-optimized key services, modular assurance for hybrid deployments, or crypto-agility tooling that simplifies transition planning. The real contest will be over specification influence: vendors that help buyers translate compliance requirements into operational architectures will shape demand more than those that compete solely on feature parity.
Future Trends to Watch
Over the next three to five years, three trends are likely to shape the commercial encryption market most directly. First, FIPS 140-3 compliance will become a default procurement baseline rather than a differentiator, and the competitive advantage will shift toward breadth, speed of validation, and the ability to support hybrid and cloud-native deployments. Vendors with completed portfolios and clear migration support will gain preference in regulated sectors, while late movers risk exclusion from specification lists.
Second, post-quantum readiness will move from policy direction to operational planning. Migration inventories, crypto-agility architectures, and hybrid key management approaches will increasingly appear in enterprise and public-sector roadmaps. Commercial opportunity will emerge for providers that can simplify transition paths, support hybrid modes, and offer clear documentation and testing for algorithm flexibility. The associated risk is fragmentation: without common deployment patterns or interoperability expectations, early implementations may require expensive integration work and create vendor lock-in concerns.
Third, encryption will continue to converge with platform services. Managed cloud HSM, integrated key protection, and data security platforms will become the primary consumption model for a growing share of commercial workloads. This trend favors players that can embed security into workflows and reduce operational overhead, but it also raises questions about long-term control of cryptographic assets, audit visibility, and portability across environments. The opportunity lies in architectures that preserve assurance while making protection easier to consume; the risk lies in over-reliance on opaque or tightly coupled services that complicate governance.
Strategic Actions for Decision-Makers
For manufacturers and product vendors, the near-term priority is to align certification roadmaps with procurement reality. Completing FIPS 140-3 validation, clarifying payment and general-purpose coverage, and communicating migration support can influence specification outcomes in regulated demand channels. Vendors should also invest in integration and cloud compatibility, because assurance alone is unlikely to win deals where operational fit is weak. Differentiation should be expressed through portfolio consistency, deployment flexibility, and clear guidance for post-quantum transition planning.
For investors and strategic partners, the most informative signals are certification milestones, ecosystem partnerships, and evidence of adoption in cloud or platform services. Companies that combine validated hardware with usable key management and data protection integration are better positioned to capture recurring commercial demand than those competing primarily on price. Portfolio exposure should be assessed not only by product footprint but by the ability to serve regulated, high-assurance, and cloud-scale segments simultaneously.
For procurement and security leaders, the practical move is to treat encryption as a lifecycle decision rather than a point purchase. Early specification of FIPS 140-3 requirements, evaluation of crypto-agility options, and review of vendor support for post-quantum transition planning will reduce downstream risk. Buyers should also assess integration fit with existing cloud, identity, and data security environments to avoid new operational bottlenecks. Where demand is complex or region-specific, detailed segment intelligence can shorten evaluation cycles and improve specification accuracy. The broader market dynamics, segment differentiation, and vendor-level developments can be explored in depth through a complete market study that provides the detailed segmentation, competitive tracking, and scenario-based guidance needed for tailored planning.
For detailed analysis of this topic, please visit the official page: Commercial Encryption Products Market
Lacy Lee
Senior Marketing Manager
sales@pmarketresearch.com
00852-95632430
PW Consulting: www.pmarketresearch.com