

@pmarketresearch
- Followers 0
- Following 0
- Updates 5116
PW Consulting: DevSecOps Tool Market Hits $10.1B in 2025, surging 27.14% CAGR Through 2032

The DevSecOps Tool Market in 2026: Strategic Intelligence for Enterprise Decision-Makers
The Imperative of Embedded Security
The software delivery landscape has fundamentally shifted. Security is no longer a final checkpoint before deployment; it is an intrinsic property woven into every stage of the development lifecycle. As organizations accelerate their digital transformation agendas, the DevSecOps tool market has emerged as a critical infrastructure layer that determines both velocity and resilience. Our latest market research provides a rigorous examination of this rapidly evolving sector, offering enterprise leaders the clarity required to make informed technology procurement, partnership, and investment decisions throughout 2026 and beyond.
DevSecOps Tool Market
This report is not merely a retrospective analysis of market growth. It is a forward-looking strategic instrument designed to help CISOs, VP of Engineering, procurement leaders, and board-level executives navigate a vendor ecosystem that is consolidating, differentiating through AI capabilities, and responding to an intensifying regulatory environment. The insights contained within are structured to translate raw market dynamics into actionable decision frameworks.
Understanding the Scale and Trajectory of the Market
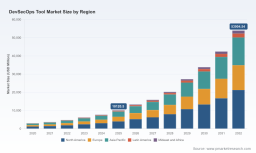
The DevSecOps tool sector has experienced an extraordinary growth arc over the past half-decade. Between 2020 and 2025, the overall market expanded from a modest base to surpass the one billion dollar threshold, reflecting the compounding impact of cloud migration, regulatory pressure, and the mainstreaming of security-left practices. The momentum does not decelerate. Forecasts extending through 2032 indicate a sustained compound annual growth rate that underscores the structural rather than cyclical nature of this expansion.
For enterprise planners, this trajectory signals more than just vendor opportunity. It indicates that DevSecOps is transitioning from a competitive differentiator to a baseline operational requirement. Organizations that delay foundational investments risk falling behind peers who are already embedding automated scanning, policy enforcement, and continuous compliance into their delivery pipelines. Conversely, enterprises that approach tool selection with strategic discipline can achieve meaningful reductions in technical debt, operational friction, and exposure windows.
Our research models multiple forward scenarios to account for variables such as procurement cycle shifts, platform consolidation trends, and the emergence of AI-assisted security workflows. Rather than presenting a single deterministic forecast, the report equips leaders with a range of plausible outcomes, enabling scenario-based budgeting and vendor negotiation strategies that remain robust under uncertainty.
What the Research Delivers: Operational Content and Decision Frameworks
Deep market intelligence achieves its value only when it is directly applicable to operational decision-making. This study is structured to bridge the gap between high-level market awareness and the granular evaluations that procurement and engineering teams must perform. The following components define the analytical core of the report:
- Comprehensive platform capability mapping that evaluates how leading solutions address static analysis, software composition analysis, dynamic testing, infrastructure-as-code validation, container security, and correlated risk visibility across the full software development lifecycle.
- Deployment architecture analysis contrasting cloud-native delivery models with on-premise and hybrid patterns, including considerations around data residency, integration complexity, and total cost of ownership over multi-year horizons.
- Industry vertical applicability assessments that identify which solution categories align best with the regulatory and operational profiles of sectors such as financial services, healthcare, government and defense, telecommunications, and retail.
- Vendor consolidation and platformization evaluation, helping enterprises determine when to pursue integrated suites versus specialized point tools, based on organizational maturity, existing technology debt, and internal skill distribution.
- Procurement and negotiation intelligence that translates market positioning trends into practical guidance for license structuring, multi-year commitments, and service-level expectations.
- Operational efficiency benchmarking that quantifies the impact of automation maturity on developer workflows, including the hidden labor costs associated with manual approvals and redundant scanning processes.
These components are designed to be referenced during tool evaluation, architecture planning, and budgeting cycles. Each section is grounded in observable market signals, vendor behavior, and procurement patterns, allowing leaders to use the report not as a one-time read but as an ongoing reference during strategic planning.
Competitive Landscape: Platform Strategy, Differentiation, and Consolidation Signals
The vendor ecosystem in the DevSecOps space is characterized by a mix of established platform players, specialized security innovators, and large enterprise software vendors extending into developer-centric security workflows. With a moderately concentrated market structure, competitive dynamics are shaped by portfolio breadth, integration depth, and the ability to reduce tool sprawl for enterprise customers.
Several platform leaders define the current strategic conversation. Checkmarx continues to advance its unified DevSecOps platform approach, emphasizing correlated risk views and broad integration points across CI/CD and development environments. Snyk has positioned itself around a developer-first philosophy, extending its software composition and container scanning capabilities into secure AI software development through its AI Trust Platform. GitLab remains a powerful all-in-one delivery and security model for organizations seeking tightly integrated pipelines with built-in testing and compliance functionality.
On the cloud-native side, Aqua Security has built a strong reputation in container, Kubernetes, and serverless protection, while increasingly expanding into supply chain security for delivery pipelines. Palo Alto Networks, through its Prisma Cloud offering, provides a code-to-cloud perspective with compliance automation and broad multi-cloud visibility, appealing to organizations seeking centralized governance. Veracode maintains a strong enterprise footprint in application security testing, integrating static, composition, and dynamic capabilities into large-scale DevSecOps workflows. OpenText focuses on connecting tools, data, and teams across the full delivery lifecycle, emphasizing integration and lifecycle orchestration. Wiz has gained traction with a cloud-native platform that supports infrastructure-as-code scanning and runtime protection, reinforcing the code-to-cloud movement.
Recent activity illustrates how quickly strategic positioning evolves. Snyk expanded its AI security capabilities through acquisition, reinforcing its focus on secure AI software development. Aqua Security introduced new protections targeting AI workloads, reflecting the broader industry effort to secure next-generation application patterns. Partnerships are also reshaping workflow dynamics, with cloud platform providers and DevSecOps vendors collaborating to accelerate developer productivity and security integration. Together, these developments highlight a market where differentiation is increasingly tied to AI readiness, pipeline integration, and lifecycle coverage.
Market Dynamics: Regulation, Workflow Friction, and Architectural Pressure
DevSecOps adoption does not occur in a vacuum. Regulatory intervention, government guidance, and internal operational constraints are actively reshaping procurement priorities and architectural expectations.
In the public sector and regulated industries, guidance from national standards bodies and defense organizations has become more explicit about the expectations for secure software development and continuous operations. Recent publications have emphasized risk-based approaches aligned with established secure software development frameworks, reinforcing the need for traceable controls and repeatable security practices. Updates to defense enterprise guidance have further highlighted platform capability expectations and compliance program alignment, signaling that procurement in sensitive sectors will increasingly favor solutions with demonstrated governance integration. At the same time, cybersecurity risk management constructs are shifting toward continuous monitoring models that fit naturally into DevSecOps pipelines, requiring tools that can support ongoing compliance evidence rather than point-in-time assessments.
On the operational side, workflow efficiency is emerging as a decisive adoption factor. Engineers and security professionals are reporting significant time losses to manual approvals, duplicate scanning, and poor tool coordination. These inefficiencies do not merely slow delivery; they erode the business case for security tooling by increasing friction without reducing risk. Organizations that select platforms solely on feature checklists, without considering workflow integration and developer experience, often find themselves paying for capability they cannot operationalize effectively. Our research addresses this reality by incorporating assessment criteria that reflect integration smoothness, automation depth, and the practical burden placed on delivery teams.
Worldwide Database Testing Tool Market
Strategic Recommendations for 2026 Enterprise Planning
Enterprise decision-makers evaluating DevSecOps investments in 2026 should approach the market with a structured lens that balances security outcomes, delivery efficiency, and long-term platform viability. The following strategic priorities emerge from the research:
- Treat DevSecOps procurement as a platform architecture decision, not a point-tool purchase. Evaluate how well candidate solutions reduce fragmentation across scanning, dependency management, infrastructure validation, and runtime protection.
- Factor AI readiness into vendor selection. The integration of AI-assisted security workflows, secure development support, and workload protection for AI-enabled applications is rapidly becoming a differentiating capability rather than a niche enhancement.
- Align tool selection with regulatory exposure. Organizations operating in or serving heavily regulated sectors should prioritize solutions with clear compliance mapping, auditability, and continuous monitoring alignment, especially where guidance is moving toward lifecycle-based risk management.
- Quantify operational burden before committing. The hidden labor costs associated with inefficient approvals and duplicate processes can undermine the return on security investment. Platforms should be assessed for their ability to streamline developer workflows rather than add procedural overhead.
- Plan for multi-year integration evolution. The most effective DevSecOps environments are built through incremental orchestration, not a single procurement event. Budget and roadmap planning should account for integration effort, internal enablement, and the likely need to consolidate tools as platform capabilities mature.
- Use market concentration dynamics to inform negotiation strategy. A moderately consolidated vendor landscape creates both opportunities and risks. Enterprises should evaluate whether suite-based platforms or best-of-breed combinations better fit their maturity level, internal skill base, and tolerance for integration complexity.
Why This Research Matters Now
The DevSecOps tool market is entering a phase where strategic clarity determines execution advantage. Growth is strong, vendor positioning is shifting, and the regulatory and operational context is becoming more demanding. In this environment, organizations need more than a list of tools or a surface-level market summary. They need a disciplined, evidence-based view of where the market is heading, how leading vendors are differentiating, and what decision criteria will produce the best security and delivery outcomes over the next several years.
This research is designed to provide that view. It combines macroeconomic trajectory with operational depth, competitive analysis, and market dynamics that shape real procurement choices. For leaders preparing budgets, architecture roadmaps, and vendor evaluations during 2026, the report offers a structured foundation for decisions that are both defensible and forward looking.
Access the Full Intelligence
The overview presented here provides the strategic framing and analytical direction of the study, but the detailed segmentation logic, capability assessments, competitive benchmarks, and scenario-based planning guidance are contained in the full report. Enterprise buyers, investors, and technology leaders who need granular market structure, vendor-by-vendor evaluation, and decision-ready frameworks will find the complete intelligence essential for informed action.
To access the complete DevSecOps Tool Market research and use it directly in your 2026 planning, review the full publication at the source page.
For detailed analysis of this topic, please visit the official page: DevSecOps Tool Market
Lacy Lee
Senior Marketing Manager
sales@pmarketresearch.com
00852-95632430
PW Consulting: www.pmarketresearch.com