

@pmarketresearch
- Followers 0
- Following 0
- Updates 5116
PW Consulting: Worldwide Application Security Solutions Market Poised for 17.22% CAGR, New Insight Report Finds

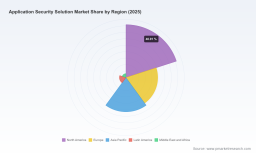
2026 Strategic Primer: Worldwide Application Security Solution Market — PW Consulting Insights
Executive summary
As enterprises prepare budgets and roadmaps for 2026, application security (AppSec) is moving from checkbox compliance to strategic enabler. Our latest PW Consulting market study — the Worldwide Application Security Solution Market — synthesizes five years of historical trends and a seven-year forecast to deliver a decision-grade perspective for security leaders, product executives, and investors. The market is in a high-growth phase, underpinned by regulatory mandates, developer-centric tooling shifts, and rapid adoption of AI-native security capabilities. Our analysis quantifies the expansion trajectory and translates it into practical guidance for procurement, architecture, and go-to-market choices in 2026.
Worldwide Application Security Solution Market
Market trajectory: scale, pace, and what the numbers mean
At a macro level, AppSec is no longer a niche cybersecurity adjunct — it is a multi-billion-dollar, fast-scaling market. PW Consulting’s base-year assessment (2025) places the global AppSec market firmly in the double-digit billion-dollar range (USD, revenue measured in millions), with a compound annual growth rate of 17.22% through the forecast horizon. Our model projects a sustained acceleration driven by cloud-native development patterns, the industrialization of software supply-chain controls, and the commercialization of runtime protection models.
Worldwide Application Security Solution Market
For decision-makers, the headline metrics mean three practical things: (1) budget allocations for AppSec will expand materially relative to adjacent cybersecurity line items; (2) vendor consolidation and specialty plays will coexist — creating both integration risk and targeted opportunity; and (3) the pace of technology change requires procurement processes that favor agility, measurable ROI, and tight DevOps integration.
Worldwide Application Security Solution Market
Why 2026 is a pivotal year
Several contemporaneous forces converge in 2026 to make AppSec selection strategic rather than tactical. Regulatory pressure — notably new European software product security mandates and U.S. requirements for software transparency in federal supply chains — elevates baseline expectations for vulnerability disclosure, SBOMs, and secure-by-design practices. Operationally, organizations face a bifurcated threat landscape: legacy monolithic applications exhibit markedly higher exploit risk, while modern microservices and serverless architectures introduce complex runtime considerations.
Concurrently, AppSec tooling itself is evolving. The market is witnessing a rapid shift to AI-assisted vulnerability discovery and remediation: a majority of forward-looking organizations are incorporating GenAI into developer workflows for code security, with vendors releasing purpose-built remediation and code-scanning features that can reduce fix times and increase developer productivity. These innovations change the calculus of tool selection — emphasis shifts to integration fidelity with CI/CD pipelines, the quality of remediation guidance, and demonstrable reductions in mean time to remediate (MTTR).
What’s inside the PW Consulting report (practical, implementation-focused)
- Methodology and data foundations: transparent modeling approach covering historical 2020–2025 activity and a scenario-based forecast for 2026–2032.
- Executive playbooks: procurement and SOW templates for evolving AppSec programs, including KPI frameworks tied to DevSecOps metrics.
- Integration matrices: decision trees that map platform capabilities (SAST, DAST, IAST, SCA, RASP, API security) to common SDLC patterns and deployment architectures.
- Vendor scorecards and capability heatmaps: comparative assessments across product maturity, DevOps fit, AI/automation, and enterprise readiness (note: detailed scorecards and numerical rankings are available in the full report).
- Implementation accelerators: 30-, 90-, and 180-day adoption roadmaps for enterprise, mid-market, and regulated organizations, including a pilot-to-scale checklist.
- Economics and ROI models: configurable templates to estimate TCO, productivity gains from automated remediation, and breach-avoidance value.
- Regulatory and compliance playbook: mapping of major regional regulatory expectations to operational controls and reporting artifacts, with a focus on SBOMs and vulnerability-handling obligations.
Competitive landscape — how to read vendor roles in 2026
The AppSec ecosystem is stratified by platform breadth, developer orientation, and runtime capability. PW Consulting’s qualitative synthesis of vendor positioning identifies four archetypes:
- Integrated AppSec platforms — vendors who offer a full SDLC suite (static, dynamic, SCA, and increasingly IaC and API security) and aim for enterprise standardization across development teams.
- Developer-first innovators — lightweight, developer-integrated tools that prioritize fast feedback loops, IDE plugins, and frictionless onboarding to catch vulnerabilities early in the pipeline.
- Runtime and production defenders — solutions focusing on RASP and runtime monitoring to provide real-time detection and mitigation for live systems.
- Supply-chain and SCA specialists — platforms focused on open source governance, license compliance, and dependency risk management, especially relevant given SBOM mandates.
Representative vendors span these archetypes. Some provide broad suites that map well to centralized AppSec programs; others prioritize speed-to-fix and developer experience. Recent industry developments underscore this shift: vendors have launched AI-powered remediation engines that materially reduce time-to-fix, integrations with major code-assist tools to secure AI-assisted development, and strategic M&A to bolster supply-chain security capabilities. Additionally, a number of vendors have achieved or pursued cloud security authorizations that facilitate adoption in regulated and government environments.
Market concentration metrics show a mid-level consolidation pattern: a handful of incumbents hold meaningful shares, but there remains substantial room for specialization and new entrants. This dynamic is shaping commercial models — buyers can expect both scale benefits from large platform providers and targeted value from best-of-breed specialist vendors.
Strategic imperatives for 2026 — recommendations for leaders
- Embed AppSec in developer workflows, not just gate checks. Prioritize tools with IDE and CI/CD integrations and measurable developer productivity gains.
- Adopt an outcomes-first procurement metric set: reduce exploitable vulnerabilities in production, compress MTTR, and demonstrate SBOM coverage where required.
- Balance prevention and detection. Combine SAST/SCA investments early in the pipeline with runtime defenses to manage residual risk in production.
- Plan for AI-driven change. Evaluate vendor roadmaps for GenAI remediation, LLM integrations, and the controls necessary to trust AI-assisted fixes.
- Operationalize supply-chain visibility. Ensure that procurement and third-party risk functions can consume SBOMs and enforce policy through automated gates.
- Design for regulatory adaptability. Align controls to upcoming mandates to avoid costly rework and to use compliance as an accelerator for secure development practices.
90-day tactical blueprint
For executive teams needing immediate traction, PW Consulting recommends a focused, three-step 90-day plan:
- Week 1–3: Rapid landscape audit — map current AppSec tooling, identify overlap, and quantify key metrics (scan coverage, false-positive rates, MTTR).
- Week 4–8: Pilot selection — choose two tools from different archetypes for parallel pilot: one developer-first and one runtime/SCA specialist. Measure friction and remediation velocity.
- Week 9–12: Scale decision and governance — apply procurement templates, finalize KPIs, and define automated gates for CI/CD linked to SBOM and vulnerability thresholds.
Why this report matters to procurement, security, and product teams
PW Consulting’s study is designed to be operationally useful. Beyond market sizing and trend analysis, the report supplies procurement-ready artifacts, vendor diligence checklists, and configuration-level guidance that reduce time-to-decision. Importantly, it bridges board-level risk framing with developer-facing process design — enabling cross-functional buy-in for AppSec investments. For investors and M&A teams, the report highlights where consolidation and specialization will drive valuation premiums over the next three years.
Guiding principles for interpreting our findings
- Context matters: vendor fit is a function of application architecture, team skill sets, and regulatory exposure — there is no one-size-fits-all “market leader” for every enterprise use case.
- Measure what matters: move beyond raw vulnerability counts to business-aligned KPIs such as exploitability, time-in-state, and developer remediation velocity.
- Plan for adaptability: expect iterative retooling as AI features and regulatory definitions evolve; prioritize modular contracts and APIs for toolchain flexibility.
Next steps — where to get the full intelligence
This release is a strategic primer designed to orient 2026 decisions and to surface the immediate operational implications of a rapidly growing AppSec market. The full PW Consulting report contains detailed segmentation data, vendor scorecards, model assumptions, and downloadable implementation assets—insights that will materially shorten vendor selection cycles and implementation timelines. To access the complete dataset and proprietary appendices (including our region and solution splits, and the full list of ranked vendors), please visit the PW Consulting report landing page.
PW Consulting’s Worldwide Application Security Solution Market study is tailored for leaders who need both macro clarity and hands-on execution guidance. In a market expanding at a robust CAGR and transforming under regulatory and technological pressure, proactive strategy and disciplined execution will separate leaders from laggards in 2026.
For detailed analysis of this topic, please visit the official page: Worldwide Application Security Solution Market
Lacy Lee
Senior Marketing Manager
sales@pmarketresearch.com
00852-95632430
PW Consulting: www.pmarketresearch.com